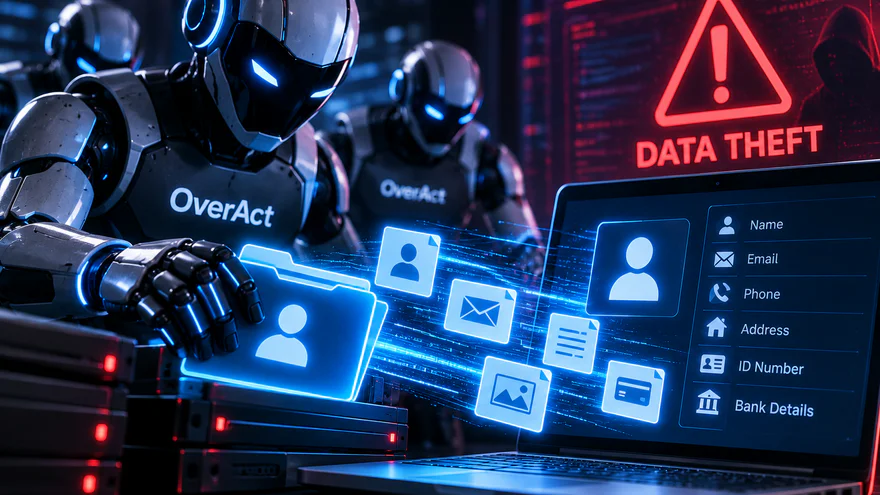
Researchers from China described a behavior where an AI agent with access to external tools requests more personal data than necessary for the task. This effect was observed in all seven tested models. The work is called OverAct, and its authors proposed a way to limit the agents' appetite: without access to the correct answer, it cuts excessive requests by almost half. The study was highlighted by the author of the Superman blog on X. According to him, developers give the assistant access to a calendar, file, or database and expect adherence to the principle of least privilege, but the model pulls everything it can reach. He calls this behavior drift rather than a malfunction: the system aims to solve the task at any cost and perceives restrictions as obstacles. The authors themselves phrase it more gently, speaking of expanding actions beyond what is directly implied by the user's words.
The article was prepared by Taolin Zhang and Jiuheng Wan from Hefei University of Technology, Hanyue Wang and Tingyuan Hu from East China Normal University, and Chengyu Wang from Alibaba Cloud Computing. The authors compiled a set of OverAct tests: eight areas with sensitive personal data, evaluation according to clear rules, without a judge model. Seven models from four families were tested, and all exceeded the allowed boundaries. In an example with a banking agent, the user asks to check the balance, but the assistant additionally retrieves transaction history, savings account data, and card information. In another case, a question about a doctor's appointment triggers the download of medications, test results, and diagnosis history. The main influence was the specificity of the request: the more vague the wording, the broader the agent interprets its powers. The more tools available, the slower the redundancy grows, and randomness in settings has almost no effect. Conclusion: the cause lies in the nature of the agent, not in random generation.
In response, the authors proposed the SelfAudit method. It works during generation and does not require retraining: the agent must justify each request with a reference to the user's task, and unjustified requests are preemptively filtered out by the system. Analysis showed that the main effect is given by filtering, not explanation. Excess requests for personal data drop by 43%. In the context of regulation: Norway was the first to restrict the wearing of AI glasses in parks, museums, shopping centers, and places with changing rooms, and a deputy from Kazakhstan, Ekaterina Smyshlyaeva, noted that she trains models because you can only regulate what you understand. Overauthorization is a characteristic example: it does not appear as hacking or an attack, so it does not fall under standard formulations of prohibited access.
This material is prepared solely for informational purposes and does not constitute financial advice or a recommendation.
Related articles