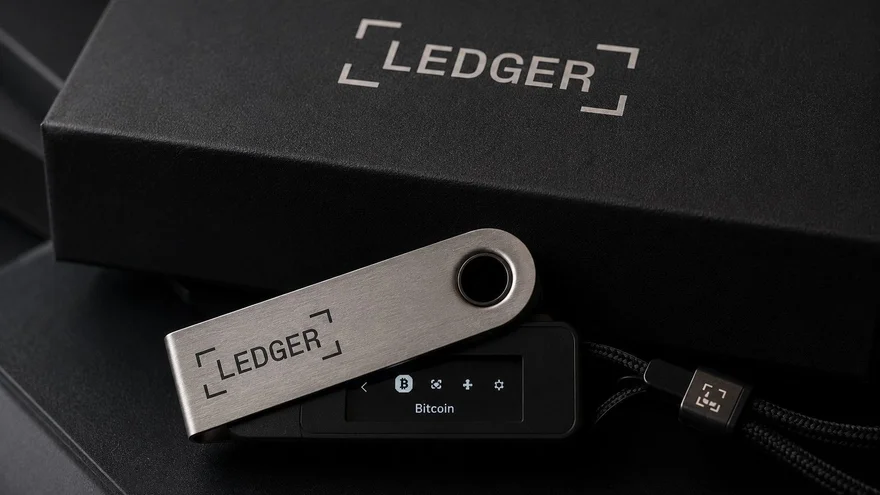
Six hardware crypto wallet manufacturers reported security issues in 2026. Cryptocurrency was lost by users in only two cases. The latest was with Ledger devices: the wallet was breached and modified before it reached the buyer.
A hardware wallet stores a secret phrase for restoring access, which manages cryptocurrency offline. In 2026, attackers attempted to target almost all chains associated with this phrase. On July 30, fraudsters began withdrawing funds from Coldcard due to a vulnerability caused by weak random key generation. Later, Galaxy Research reported that Coldcard lost over $115 million. In June, Ledger's security team conducted a laser attack on Trezor Safe 7 chips, and in July on Tangem cards. Such attacks require physical access to the device and expensive laboratory equipment. Trezor stated that users' funds were not affected. Tangem explained that the risk for ordinary users is "practically nonexistent," adding that researchers work for competitors.
In August, BitBox fixed several serious vulnerabilities in the firmware discovered by the company's engineers. No theft of funds was reported. Other incidents affected customer data but not their keys. A Trezor partner experienced a data leak of 13,689 buyers, and a SafePal breach exposed nearly 40,000 customer home addresses. Ledger confirmed on Saturday the modification of a user's device. In an update on Sunday, the company clarified that all confirmed cases relate to the Malaysian reseller CryptoBilis. On-chain analysts estimate the damage at nearly $90 million. One buyer lost 80 bitcoins just days after setting up the wallet. Ledger does not disclose the total amount of losses.
CryptoBilis has ceased sales of hardware wallets. Former co-founders stated on LinkedIn that they transferred the company to new owners back in March. Some users report that devices purchased from Ledger's official European store failed authenticity checks. Ledger has not confirmed any such cases outside the CryptoBilis store. Ledger advises purchasing devices only from the company itself or official resellers. Ledger owners from CryptoBilis are advised not to set up unused wallets and to transfer assets to a new recovery phrase. BitBox recommends timely software updates and entering recovery words only on the device itself. Trezor notes that phishing remains the most common threat. Hardware wallets cannot be called completely secure: outside laboratories, no security chip has been breached, yet Coldcard and Ledger users still lost funds.
This material is prepared solely for informational purposes and does not constitute financial advice or a recommendation.
Related articles